Ransomware at the Airport
A September 2025 ransomware attack on Collins Aerospace disrupted major European airports, a reminder that when a supplier is breached, your own business operations may stop too.
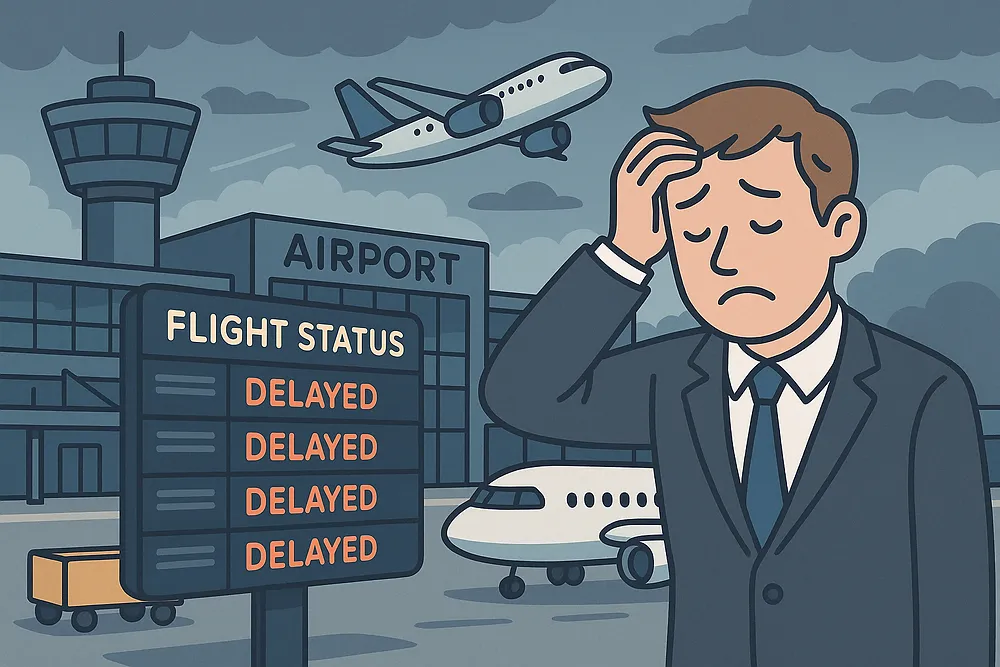
When major European airports ground to a halt in September 2025, the cause wasn’t a storm, strike, or mechanical failure. It was ransomware. Collins Aerospace, which supplies check-in and boarding systems to airports across Europe, was hit by a sophisticated cyberattack that began on Friday night (September 20, 2025). Passenger check-in and baggage systems failed at airports including Heathrow, Brussels, Berlin, and Dublin, forcing them into “manual mode” with paper boarding passes and handwritten luggage tags. Thousands of passengers were left stranded or waiting for hours.
This matters for every New Zealand business: when a supplier suffers a cyber security breach, your own operations can stop too.
What Happened at European Airports
The Collins Aerospace incident, confirmed by the European Union Agency for Cybersecurity (ENISA) as a ransomware attack, demonstrates how quickly critical infrastructure can collapse. The attack began on Friday night, and personnel at several airports were forced to switch to manual procedures, leading to long queues and widespread delays:
-
Collins Aerospace’s check-in software was encrypted by ransomware attackers, impacting multiple European airports simultaneously
-
Check-in kiosks, boarding pass printers, and baggage tag systems were completely disabled
-
Heathrow reported delays due to the technical issue affecting Collins’ software systems
-
Airports fell back on manual processes with staff writing boarding passes by hand and manually checking baggage
-
While manual systems partly worked, they created hours of delays and numerous flight cancellations
The attack shut down the cloud back-end for Collins’ cMUSE platform, highlighting how cloud-dependent modern airport operations have become.
The attack shows how a cyber security incident affecting one third-party vendor can simultaneously cripple multiple organisations that weren’t directly targeted. This is what security experts call a “supply chain attack” where criminals target a supplier to reach multiple victims at once.
Concerns in New Zealand
While New Zealand hasn’t experienced an airport ransomware attack of this scale, we’ve had several technology failures that created similar operational chaos and demonstrate our vulnerability:
Auckland Airport System Failures
Auckland International Airport has experienced multiple serious computer system failures in recent years. In August 2024, a computer system glitch forced check-ins to be suspended for several hours, leaving hundreds of travellers stranded. The airport spokesperson confirmed the check-in system experienced technical difficulties due to an external digital system, showing how dependent we are on third-party technology providers.
More recently, in December 2024, another technology issue hit Auckland Airport’s international check-in system, causing long delays during peak travel season. These weren’t cyber-related incidents, but they demonstrate how quickly airport operations can collapse when technology fails.
National Aviation System Vulnerabilities
New Zealand’s aviation infrastructure has shown other concerning vulnerabilities:
-
Air traffic control system failures: Airways New Zealand has experienced rare but significant faults in its control systems that have disrupted flights across the Tasman, causing aircraft to circle offshore while systems were restored
-
CrowdStrike global outage (July 2024): A faulty security software update brought down Windows machines globally, affecting New Zealand airports and creating widespread disruption to check-in systems
And let’s not forget the Waikato DHB ransomware attack that crippled hospitals, delayed treatments, and exposed patients’ sensitive information on the dark web.
These incidents highlight that business continuity and cyber security are now inseparable concerns. Whether the cause is ransomware, a software misconfiguration, or a faulty security update, the operational result is identical: critical business functions stop working.
What This Means for NZ Businesses
The Collins Aerospace attack is a useful prompt for any organisation to think about which of its critical business functions depend on a third-party system, and what happens if that system goes offline.
For most businesses, the list is longer than expected. Point-of-sale systems, payroll platforms, cloud accounting tools, shipping software, booking systems: a large proportion of daily operations now runs on services hosted and managed by someone else. When those services fail, whether from ransomware, a software fault, or a CrowdStrike-style update issue, the business impact is the same regardless of cause.
The question worth asking is whether you could operate if any of your critical third-party systems were unavailable for 24 hours, 48 hours, or a week. Auckland Airport’s system failures in 2024 showed what that looks like in practice: check-ins suspended, hundreds of passengers stranded, and those were technology faults, not attacks.
In practice, this means knowing what your critical dependencies are, having a manual fallback for the most important processes, and checking what your SaaS and cloud vendors’ own security and business continuity arrangements look like before you need to rely on them. Vendor security questionnaires and contract provisions around incident notification are more relevant than most businesses give them credit for, right up until a supplier goes down and you are waiting on their status page to find out what is happening.
Who this hits hardest in New Zealand
Some sectors carry more of this risk than others. Tourism and hospitality run on online booking and payment platforms, hold passport and card details, and feel an outage most during peak season. Farming and primary industry now depend on precision-agriculture software, IoT devices and supply-chain systems that link farms to processors. Law firms, accountants and consultancies hold confidential client data, rely on billing and document systems, and their trusted-advisor role makes them a target for social engineering. The common thread is the same: core work stops when a third-party system goes down.
Building a security culture
Technical controls are only part of the answer. Train staff to spot phishing, make it safe to report mistakes, and put cyber risk on the board’s agenda alongside the budget for the tools and training to deal with it.
The Collins Aerospace ransomware incident serves as a warning for every New Zealand business, regardless of size or industry. The attack, which ENISA confirmed as ransomware, demonstrates how quickly operations can collapse when third-party systems fail.
In New Zealand, we’ve already experienced how system failures can disrupt everything from air travel to retail operations. The Auckland Airport incidents in 2024 showed how hundreds of travellers can be stranded when check-in systems fail, even without malicious intent. Add ransomware into this equation, and the stakes become much higher.
Ask every critical supplier one question: if your system went down for a week, how would we keep trading? Then map your dependencies, test your fallback plans, and make sure you can keep operating when a critical supplier fails.
Cyber security is business continuity. The businesses that prepare for a supplier outage are the ones still serving customers while others are waiting on a status page.
Supply chain attacks and vendor failures will reach New Zealand businesses. The first step is a list of the third-party systems your business cannot run without.
This article was updated in September 2025 to reflect the latest cyber security incidents affecting international and New Zealand infrastructure. For more information on cyber security resources for New Zealand businesses, visit the CERT NZ website.